Whitehats move 52 bitcoin from the Coldcard hack to a recovery trust
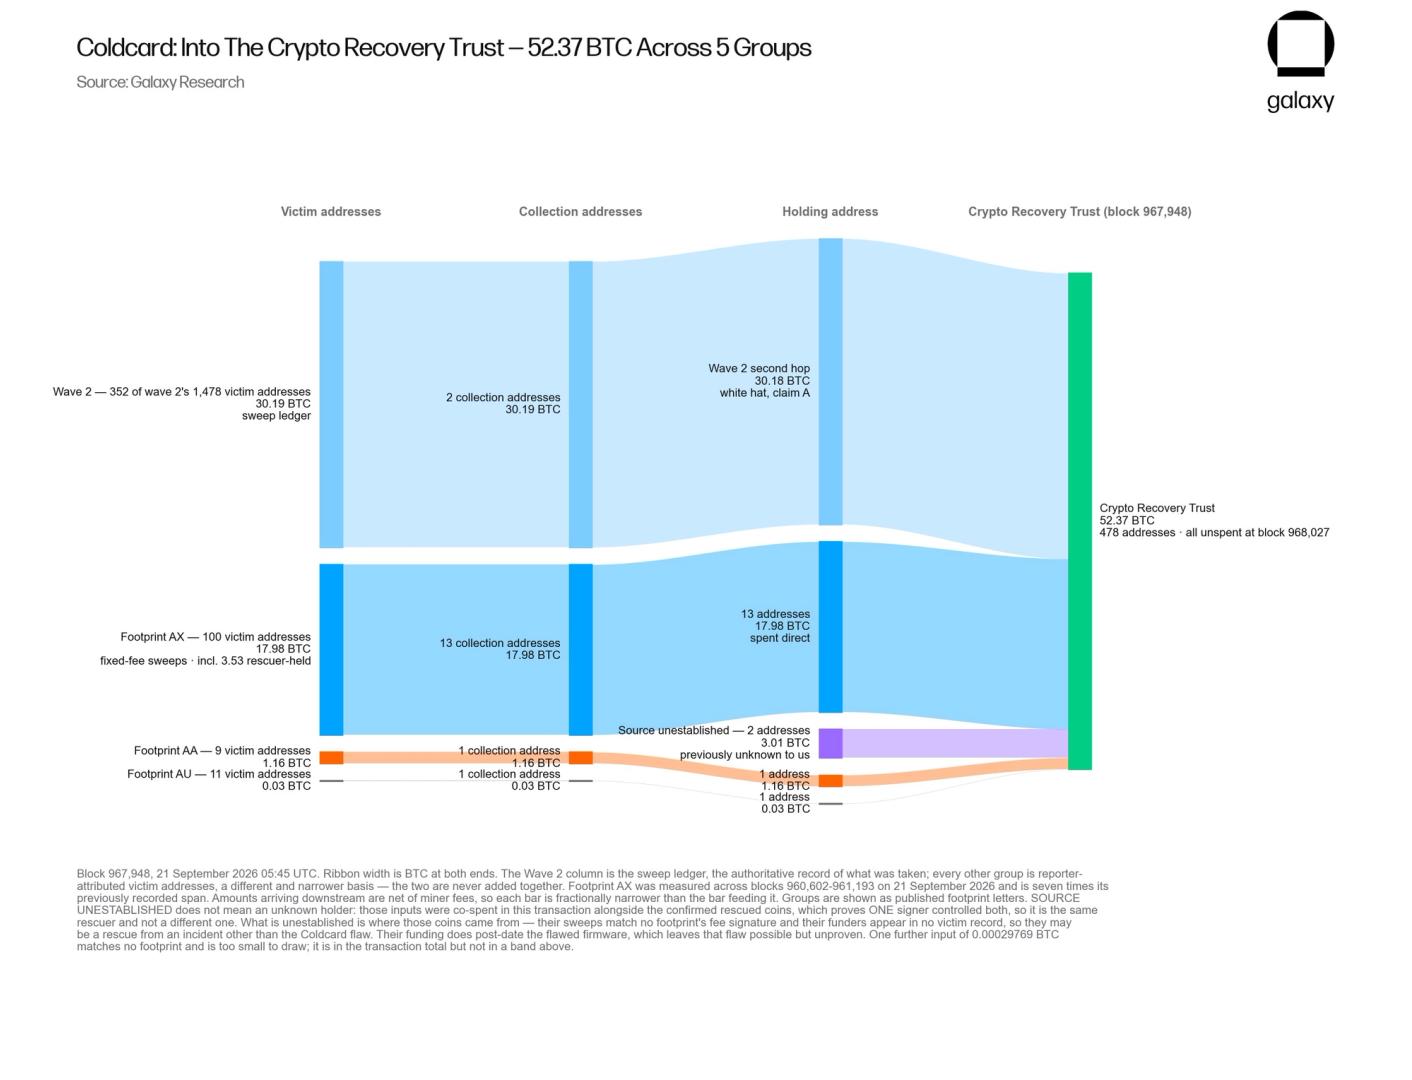
According to Galaxy Digital, the good guys have moved 52 BTC to an address carrying an OP_RETURN message reading "claim:cryptorecoverytrust dot com."
“Whitehat operators” have moved 52.37 BTC to an address linked to a newly formed recovery trust, as part of the ongoing fallout from July's Coldcard hardware wallet exploit, according to Galaxy Digital's Head of Research Alex Thorn.
The Coldcard crypto hardware wallet hack began on July 30, with multiple batches (waves 1, 2, and 3) of attacks in subsequent days resulting in estimated losses of over $100 million in bitcoin BTC$85,437.23.
Attackers exploited this, causing wallets to generate seeds using a weaker software-based random number source instead of the wallet’s dedicated random number generator. That made some seeds vulnerable to reconstruction by hackers.
Coinkite, the maker of Coldcard, has since patched the firmware, though funds already exposed under the old seeds remain at risk regardless of the patch.
According to Thorn, some of the coins moved out of victim wallets weren't taken by malicious actors but by whitehats, or ethical cybersecurity professionals who use hacking skills to find and fix security weaknesses.
These so-called good guys swept the funds specifically to keep them safe until they could be returned.
The 52.37 BTC moved this week represents such a sweep, consolidated from Wave 2 of the tracked exploit funds along with three footprints labeled AA, AU and AX, and sent to an address carrying an OP_RETURN message reading "claim:cryptorecoverytrust dot com." The transaction was confirmed in block 967,948.
Thorn said the amount represents 2.8% of the total tracked exploit funds and that roughly 40% of Wave 2 has now been identified as whitehat activity. An additional 3.0134 BTC with no prior tracking history also flowed into the CRT address in the same transaction. Thorn said this is presumably additional white-hat-recovered Coldcard funds, though he stressed this remains unconfirmed.
Victims can check whether their funds were among those recovered by visiting cryptorecoverytrust.com and searching their addresses.
As stablecoins move into regulated finance, APAC is becoming a key proving ground. This report maps the region’s rules, use cases, and RLUSD’s role.
Asanat Analysis — Why it matters
The movement of 52 BTC from a Coldcard hardware wallet exploit to a recovery mechanism signals an emerging operational pattern in crypto security incident resolution. Rather than funds disappearing into laundering pipelines, whitehat actors are now establishing transparent recovery infrastructure—the OP_RETURN metadata creates an on-chain record of intent and destination. This suggests growing maturity in the ecosystem's ability to coordinate post-breach asset recovery, though the efficacy depends entirely on whether cryptorecoverytrust.com operates with legal standing and affected user KYC data.
Coldcard's recurrence in security incidents (previous exploits in 2021-2023) underscores a persistent tension: hardware wallet firmware updates lag real-world attack sophistication, and supply chain vulnerabilities remain harder to patch than software. The whitehat intervention here—rather than ransom negotiation or silent recovery—also reflects insurance or protocol-level incentives increasingly embedded in DeFi infrastructure. Watch whether this recovery model becomes standard for institutional-grade breaches or remains ad-hoc.